
Security Questions on NyquistAI MCP
Answers to common security and architecture questions from IT, security, and procurement teams evaluating the NyquistAI MCP server.
← Back to the MCP Server Guide1.MCP architecture and overall system configuration
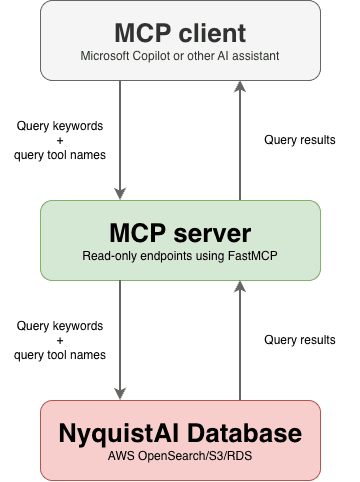
NyquistAI MCP service is using FastMCP, which is the most widely used MCP framework. Our MCP server supports read-only communication between our curated data and AI models. NyquistAI MCP service doesn't include AI models.
2.Data flow between Microsoft Copilot, NyquistAI, and any related services
In Microsoft Copilot, when a user asks a question related to medical devices or clinical trials, the AI models from Copilot (not from NyquistAI) may decide it needs information from NyquistAI to answer it. Then the AI model will do the query via NyquistAI MCP service. The Copilot AI model sends the query keyword to NyquistAI MCP and NyquistAI MCP returns query results to the Copilot AI model. NyquistAI MCP service only receives the query keyword, not the user conversations with Copilot AI models. NyquistAI MCP server doesn't receive user profiles or the AI model details.
3.Types of data transmitted and received through MCP
The Copilot AI models send query keywords to NyquistAI MCP service and NyquistAI MCP returns query results. No other information is transmitted.
4.Authentication and authorization mechanisms
NyquistAI MCP service is using OAuth 2.0 for authentication and authorization. This is the most widely used and officially recommended practice by MCP standards.
5.Permissions required for users and administrators
Users need a NyquistAI account to use our MCP service. Microsoft administrators can control which user or user group has access to NyquistAI MCP in Microsoft Copilot.
6.Data storage locations and retention policies
All NyquistAI services are hosted on AWS (us-east-1).
NyquistAI doesn't record user query history by default. When something goes wrong, we record the minimal information for debugging purposes. The error logs are permanently deleted after the issue is resolved.
7.Security controls applied to transmitted and stored data
As part of the MCP standard, all data between NyquistAI MCP and AI models is transmitted over HTTPS (TLS 1.2 or later).
All NyquistAI services are hosted on AWS, and our curated data is stored with standard encryption in S3, RDS and OpenSearch.
NyquistAI doesn't record user query history by default. When something goes wrong, we record the minimal information for debugging purposes. The error logs are permanently deleted after the issue is resolved.